Governance and compliance.
Valistry shows how ready you are for the AI and data regulations you answer to, and keeps the evidence for an audit: every AI tool, who holds it, the settings we can read, documents, incidents, and the returns as files. It reads no prompts or replies by default.
What Valistry shows
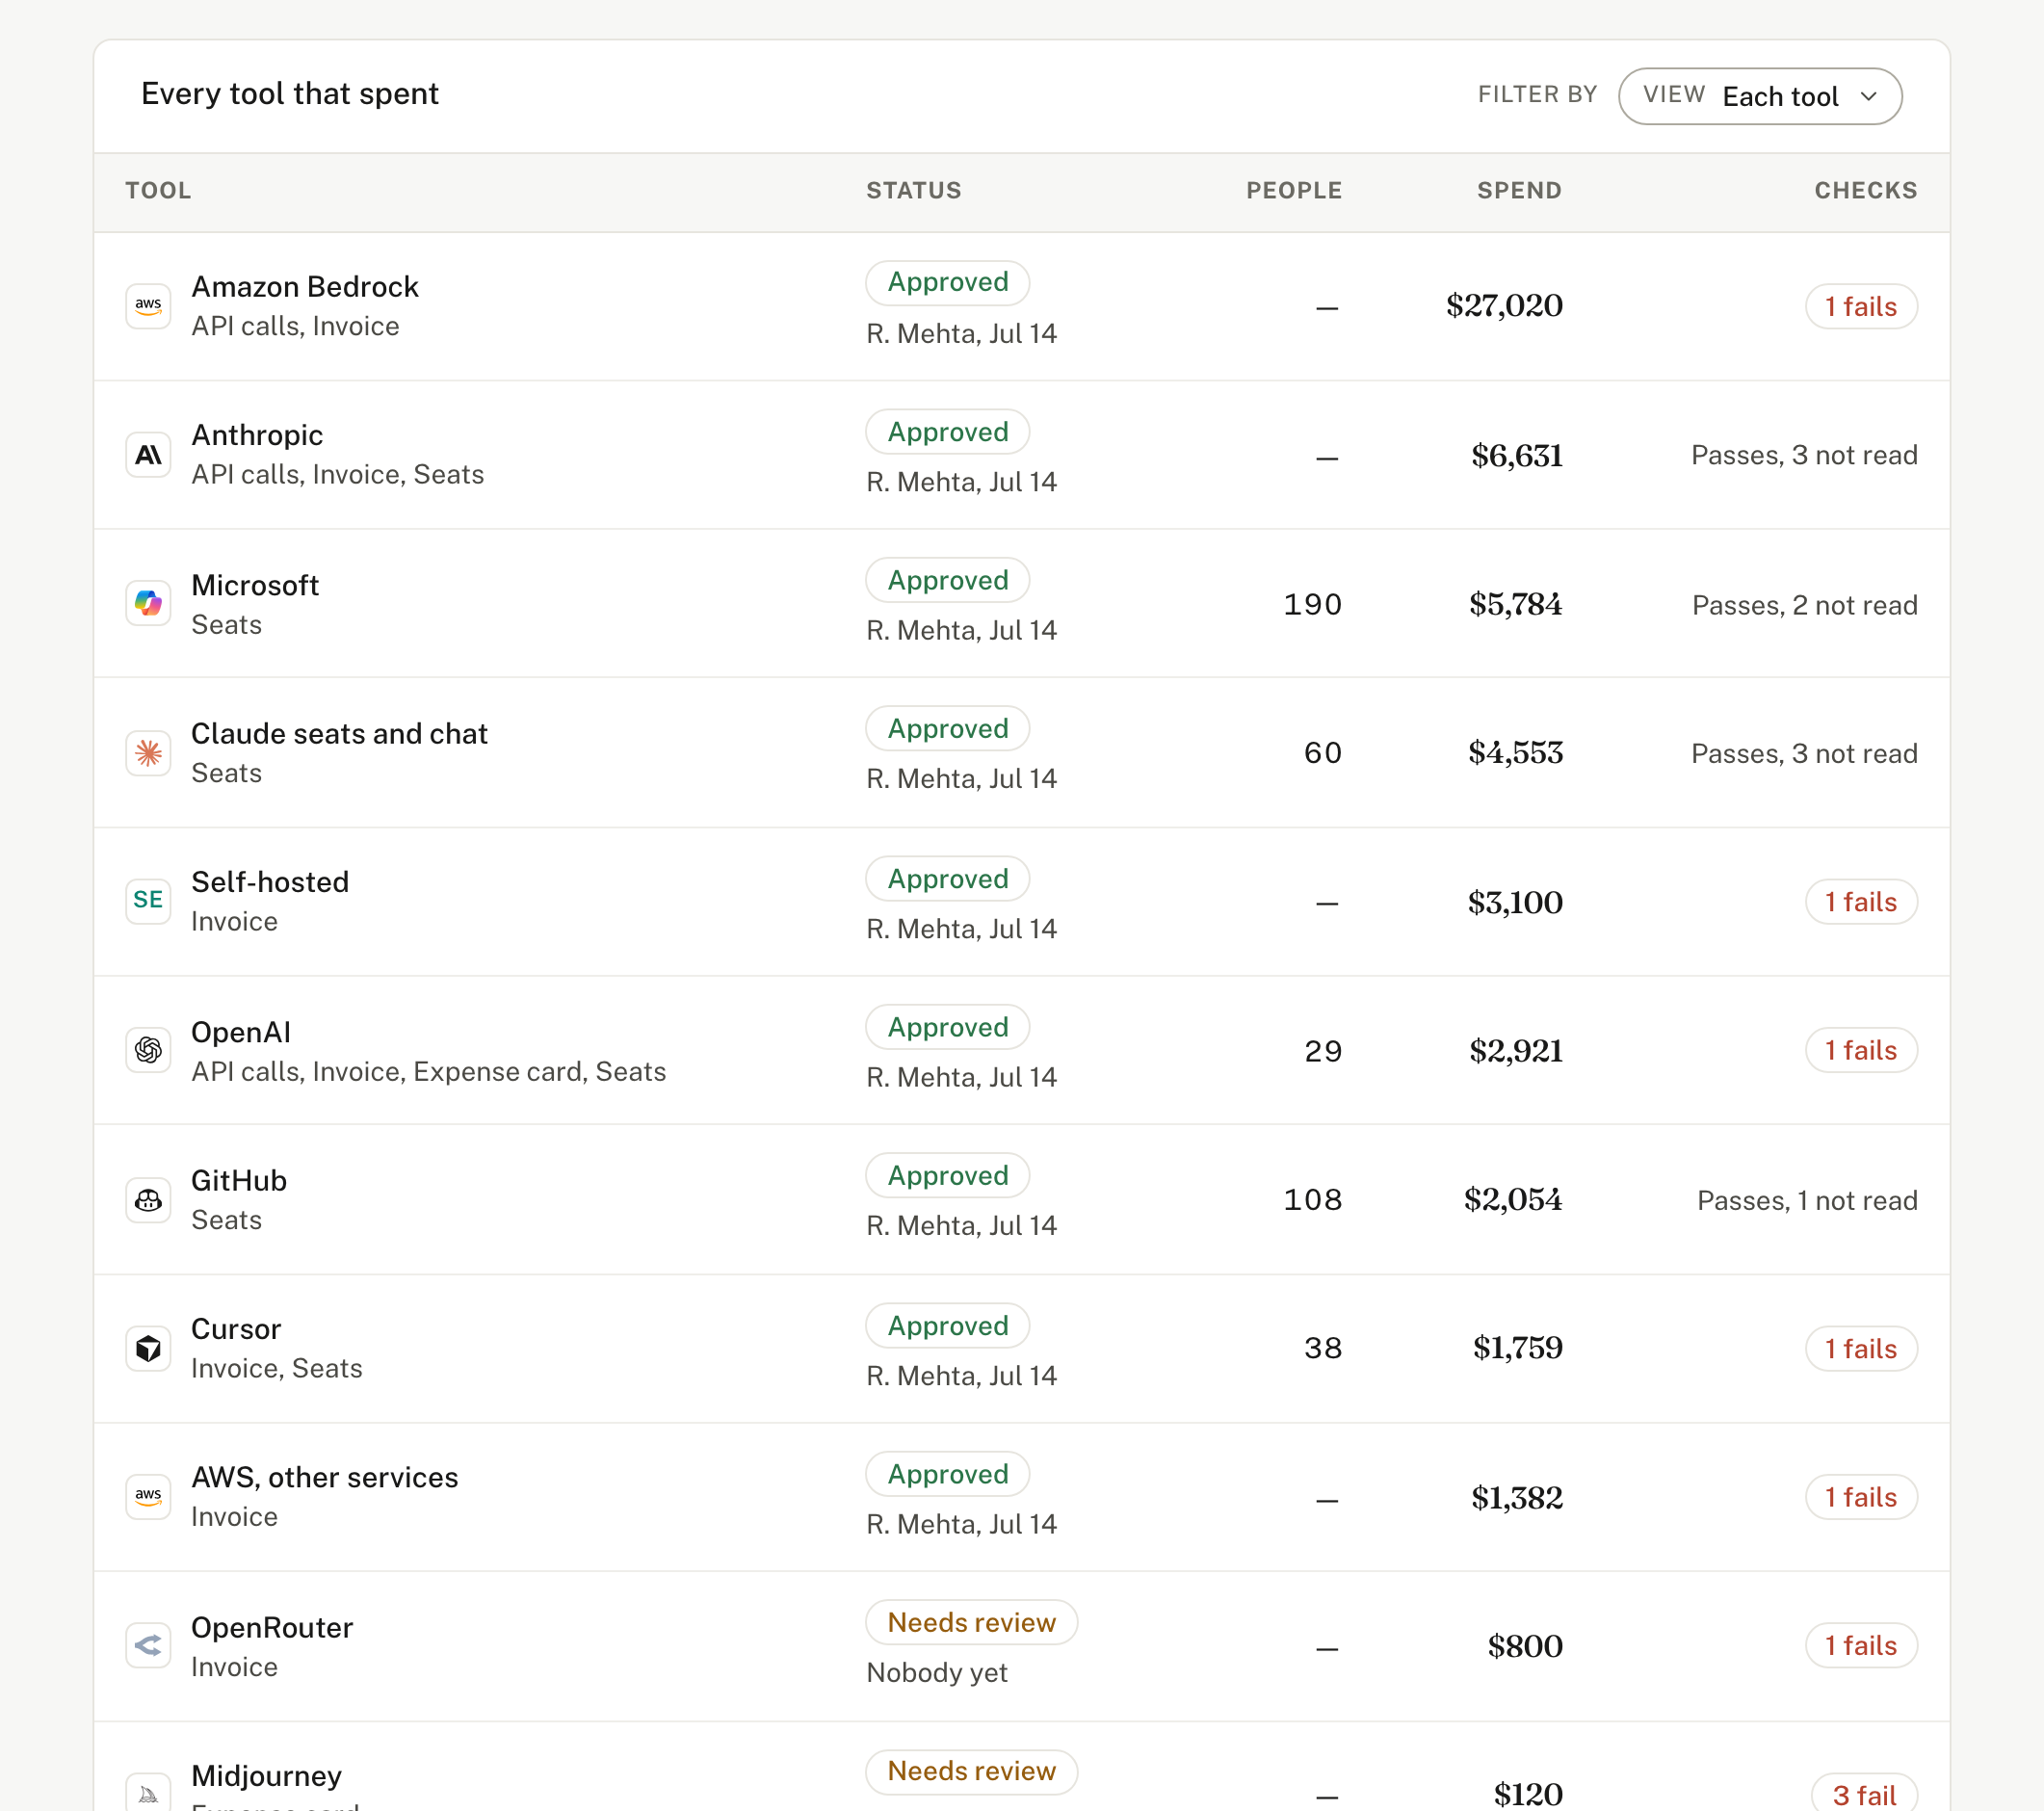
- Every AI tool in use
- Each with its status, approved, on trial, needs review or not permitted, and who decided and when. AI apps people sign in to that nobody pays for, from an Entra, Okta or Google Workspace scan: app names and counts, never a person. An ask for a new tool goes to an owner or an admin to decide.
- Checks on each tool
- Is it approved, was it bought on an expense card, does the vendor train on your data, where is your data, does it have an owner.
- The settings we read
- Three, from the vendor's own admin access: OpenAI's data retention, Bedrock's call logging, and how each AI app signs in through Entra or Okta. Each is read as on or off. A setting a vendor does not expose, such as Cursor's privacy mode or Copilot's no-training setting, says "Not read yet" with the reason.
- Who holds which AI seat
- By team. Former employees who still hold a seat, where a connected directory says who left. Agents as identities, each with an owner and its last call. An access review asks Keep or Remove for every seat, and checks the answer against the next seat list.
- Vendor profiles
- 16 AI vendors' data practices: training on your data, retention, zero retention, regions and certifications, each checked twice against the vendor's own pages.
- Documents
- The AI policy, impact assessments and data processing agreements, each with an owner and a review date, linked to the rules that ask for them. Valistry keeps a link to where each one lives, never the file.
- Incidents
- When each was found and when it was reported. A personal data breach reported more than 72 hours later is flagged.
- A change log
- Rules, policies, approvals, owners, budgets, members and sources: who changed each, and when. The decision ledger and the connector call log cannot be edited in the database; only deleting your organization erases them.
Each screen, tab by tab: Tools, Access and Regulations.
Regulations
For each: does it apply to you, how ready you are, and every gap with how to close it.
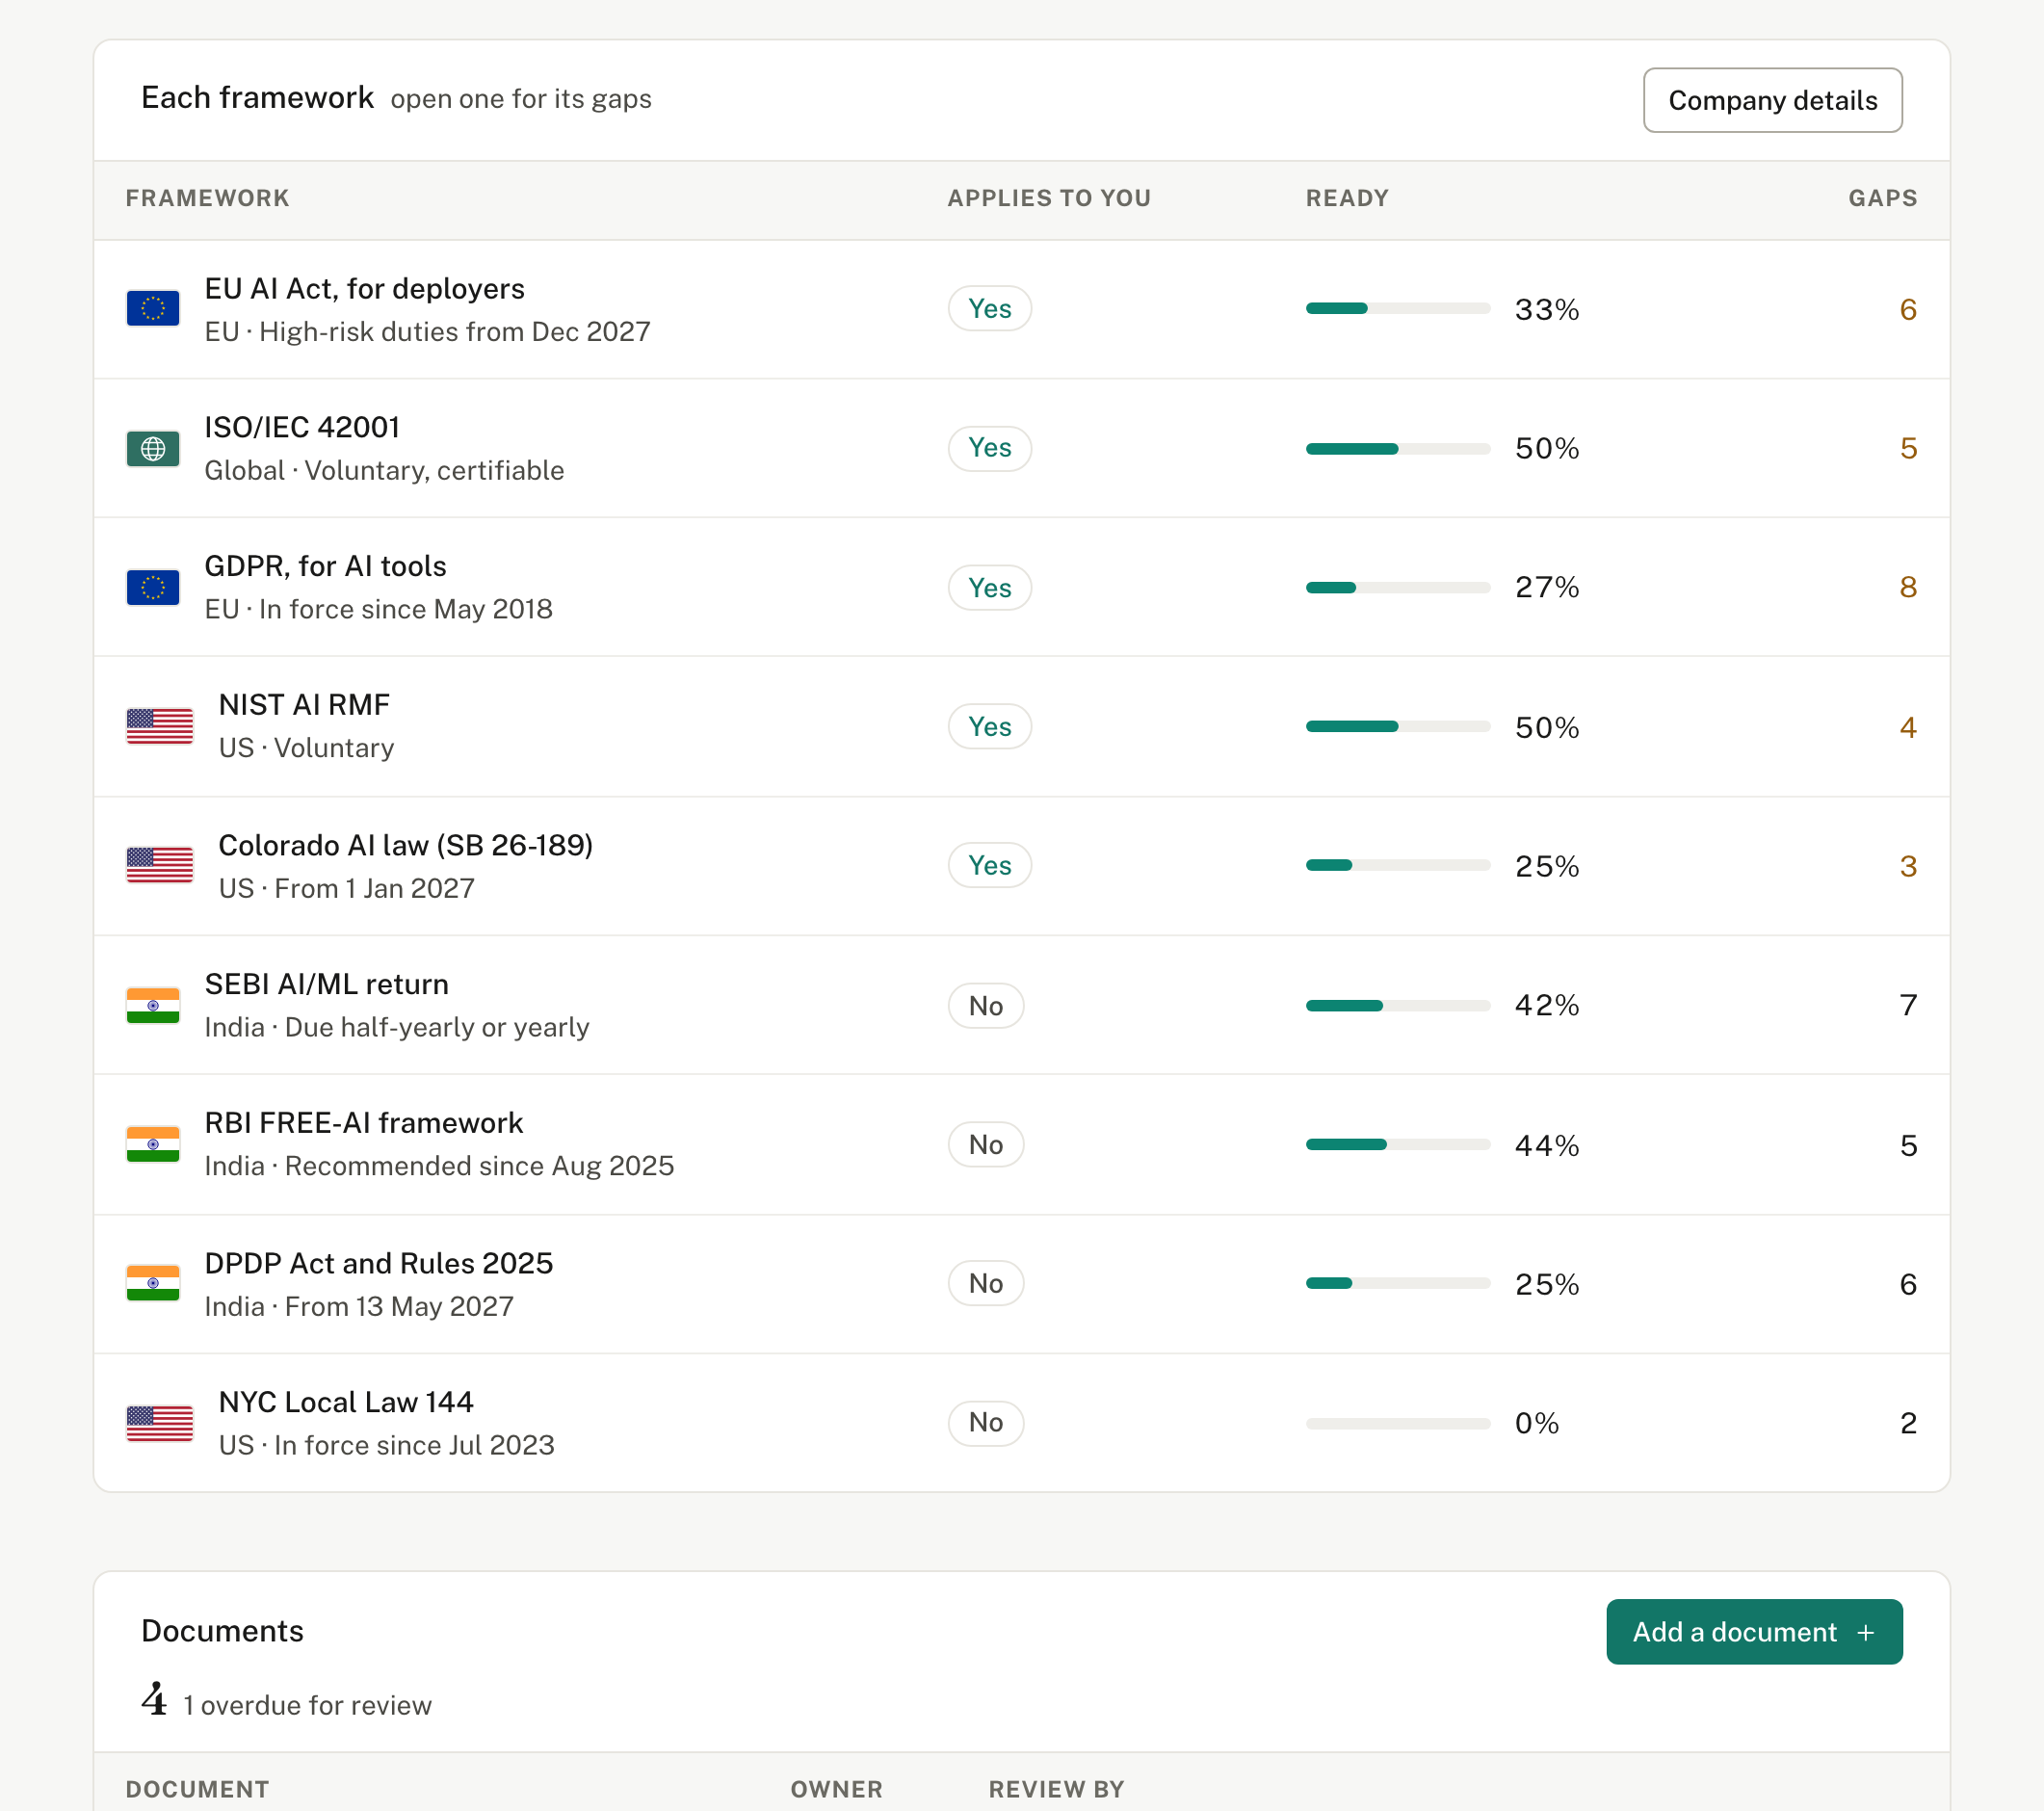
 SEBI AI/ML return
- SEBI-registered intermediaries. Half-yearly for algo brokers, yearly for others; a NIL return is due even with no AI.
- RBI FREE-AI framework
- Banks, NBFCs and other regulated entities. Recommended since 13 Aug 2025; inventory updated every six months.
- DPDP Act and Rules 2025
- Any company handling personal data in India. Duties on fiduciaries from 13 May 2027.
 EU AI Act, for deployers
- Companies using AI in the EU. Art. 50 since 2 Aug 2026; high-risk duties from 2 Dec 2027.
 ISO/IEC 42001
- Any organization running an AI management system. Voluntary standard; certifiable.
- GDPR, for AI tools
- Companies handling personal data of people in the EU. In force since 25 May 2018.
 NIST AI RMF
- Any organization; expected by US buyers. Voluntary framework.
- Colorado AI law (SB 26-189)
- Companies using AI in consequential decisions about Coloradans. Signed 14 May 2026; developer duties from 1 Jan 2027.
- NYC Local Law 144
- Employers using AI to hire or promote in New York City. In force since 5 Jul 2023.
The returns as files
Valistry's fields are filled in. A field only your company can answer says “(you)” and stays empty.
- SEBI's AI/ML return
- One row per AI system, with the fields Valistry knows filled in.
- RBI FREE-AI's AI inventory
- Every AI system with its owner, vendor and dependencies.
- GDPR Article 30 records
- Each AI tool as a processing record: vendor, regions and retention.
- Each rule's evidence
- A file per framework for an auditor: every requirement, what shows it, and what is still open.
Three frameworks, in the product
- EU AI Act, for deployers
- Compliance → Regulations shows whether it applies to you and each duty a company using AI has. Valistry shows which systems are high risk, who oversees each, the incidents and when they were reported, whether call logging is on, and which general-purpose models you use. Duties only you can confirm, such as telling workers, stay yours to mark.
- NIST AI RMF
- Its first ask is an inventory of the AI in use and who answers for it. Compliance → Tools is that inventory, kept from what you pay for and sign in to, not from a survey, with owners and decisions on every tool.
- ISO/IEC 42001
- An AI management system starts from a scope of AI systems, an owner for each, suppliers that follow your rules, and documents kept current. Tools, Access, vendor profiles and Documents show each, with every gap and how to close it.
Where it stops
- Valistry shows how ready you are
- It never makes a company compliant, certifies it, or guarantees an outcome. The evidence is for you and your auditor to judge.
- No content kept
- No prompts or replies from your AI vendors, no documents, no source code. GitHub reads hold files in memory and drop them. Settings are read as on or off; documents are kept as links. There is no field for any of it.
- Not security testing, not model risk
- Valistry does not test a model for bias, accuracy or attacks, and does not filter content. Those tools keep their own controls.
- Only what a vendor exposes
- Three settings today, named above. Where a vendor's admin access does not return a setting, the product says so rather than guessing.
- The record starts when you connect
- History before the first sync is what each vendor's API returns: ninety days for most, less for some. Each connector page says which.
Getting the record out
The change log exports as CSV and JSON, and on the Enterprise tier the same rows are posted nightly to an endpoint you name, signed.
An export never holds a source's credential: only the connector and the last four characters of the key.
How we hold your data covers residency, retention and deletion.